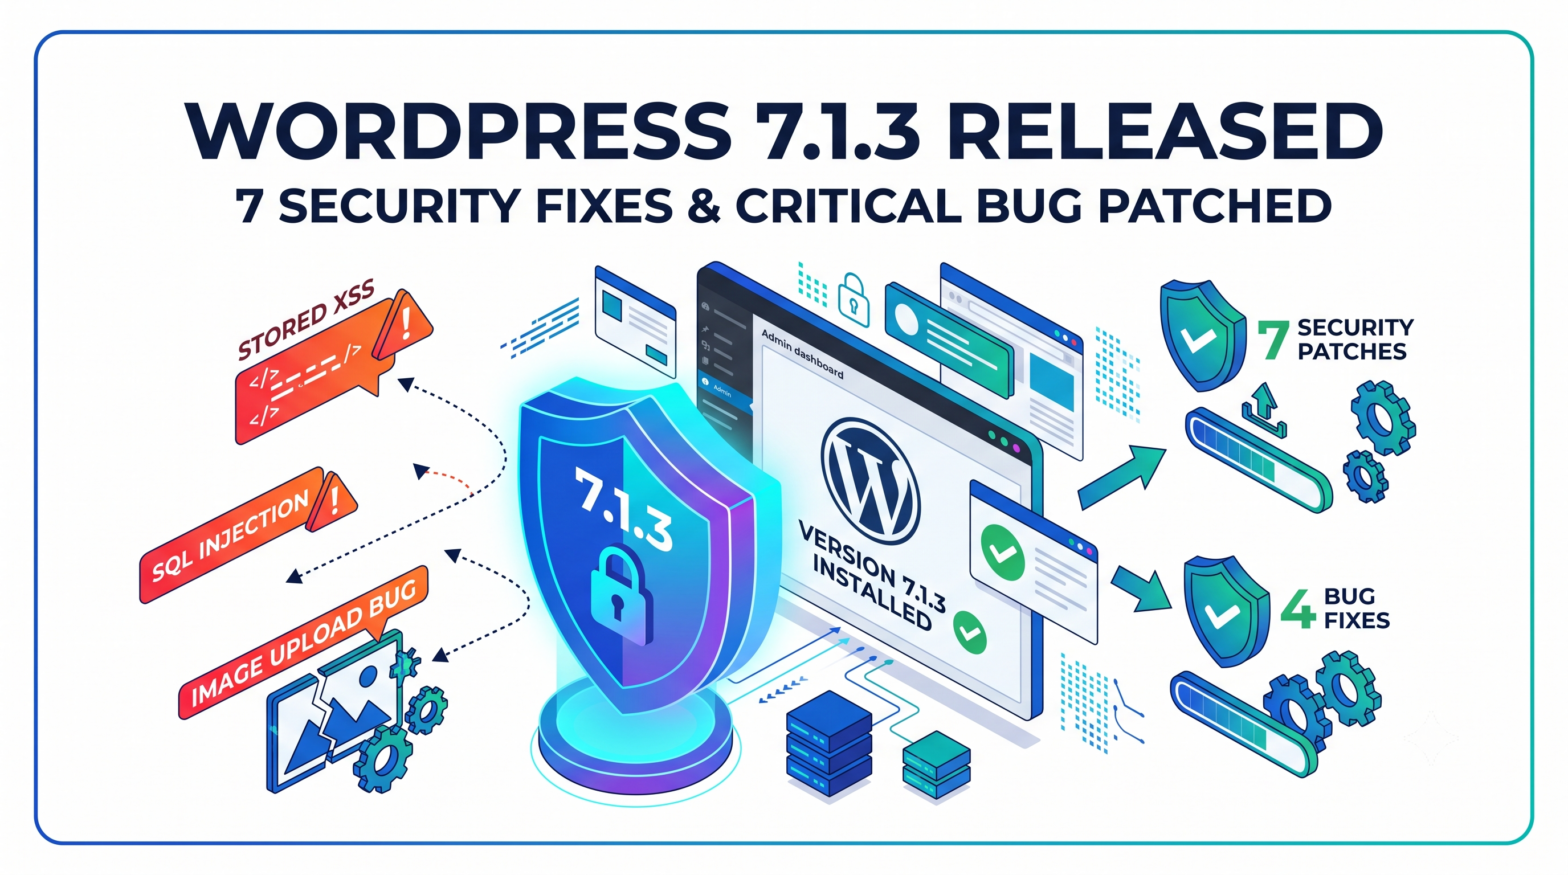
WordPress site owners on any version prior to 7.1.3 are now running software with seven known, unpatched security vulnerabilities. WordPress published version 7.1.3 on October 6, 2026, in a combined security and maintenance release that also resolves four bugs, one of which carries a critical severity rating in the project's own issue tracker.
Seven Vulnerabilities Patched Across Core
The release features seven security fixes and four bug fixes. The announcement was published October 6, 2026, and the release was led by Jake Spurlock.
No exploitation in the wild or public proof-of-concept has been confirmed for any of the issues, and WordPress has not assigned CVE numbers in its release notes.
The seven vulnerabilities named in the October 6 WordPress.org announcement are:
- A stored cross-site scripting (XSS) flaw on the Comments administration page, exploitable via pending comments, reported by Thomas Chauchefoin of Trail of Bits
- A denial-of-service (DoS) issue in the `WP_Http::make_absolute_url()` method, reported by Anthropic
- A second-order SQL injection in the WordPress WXR export feature, reported by Anthropic
- A weakness allowing users with the Author role to sticky posts, reported by Anthropic
- Unauthenticated disclosure of comments on private and unpublished posts, reported by Ananda Dhakal of Patchstack
- An XSS vulnerability in Imgur embeds, reported by Zhengyu Liu, Jingcheng Yang, and Gavin Zhong
- Forgeable parameters passed to the `{status}_{type}` hook that can lead to action name collision, reported by Alex Concha of the WordPress security team
The release announcement credits AI company Anthropic with three of the seven reports. The official announcement does not include CVSS scores, severity ratings, or descriptions of how each vulnerability operates.
Stored XSS and SQL Injection Carry the Highest Practical Risk
Two bugs allow cross-site scripting: one is a stored XSS on the Comments admin page exploitable via pending comments, and another affects Imgur embeds. A second-order SQL injection also sits in the WXR export feature.
Per Patchstack, two of the vulnerabilities start with a logged-out visitor; the Comments XSS also requires a moderator's click, three require a Contributor or Author account, and the SQL injection requires an administrator to run an export.
On the hook collision issue: prior to this release, a post saved with the status `delete` and the type `post` could fire `delete_post`, the same action as a real deletion, causing every callback hooked to it to run as if a post had been deleted. Version 7.1.3 only fires these hooks when the status and post type are registered.
Critical Bug Blocks Image Uploads on Some Hosts
Beyond the security fixes, a bug rated critical in WordPress's own issue tracker can make image uploads fail with a fatal error on hosts lacking PHP's optional DOM extension, leaving site owners unable to upload media.
The `wp_get_image_alttext()` function is invoked when uploading an image to extract alternative text embedded in XMP metadata. The function instantiates `DOMDocument()` and `DOMXPath()` without first verifying whether PHP's `ext-dom` extension is installed on the host environment, producing a fatal error when the extension is absent.
WordPress 7.0 introduced the code that used `DOMDocument` without checking whether the extension existed. On hosts without it, image uploads could trigger a fatal error and fail completely.
The scope of the problem appears limited. The WordPress ticket rates the severity as critical, but a core committer noted the code had been in production for 134 days before the first report was filed, an indicator that the extension is present on the overwhelming majority of hosting environments.
Backports and Update Instructions
Security fixes are being backported to all branches currently eligible to receive them, extending back through WordPress 4.7. Only the most recent version of WordPress is actively supported. The backports are in progress and will ship as they become ready.
As of October 6, 2026, backports had shipped through the 6.6 releases. Branches from 4.7 through 6.5 were still awaiting patches at the time of publication.
For site owners managing updates manually, WordPress recommends updating immediately. Version 7.1.3 is available from WordPress.org or through the WordPress Dashboard under Updates. Sites configured for automatic background updates will receive the update automatically.
For site owners managing multiple WordPress installations, the combination of an unauthenticated comment-disclosure flaw and a stored XSS exploitable through the comments workflow means that sites with active comment moderation queues warrant the most urgent attention when prioritizing updates.
WordPress 7.1.3 is the third security release on the 7.1 branch in 19 days: 7.1.1 shipped on September 17, 7.1.2 on September 22, and 7.1.3 on October 6.